Generative AI usage policy for companies: what it should say, in one page, and a template to start
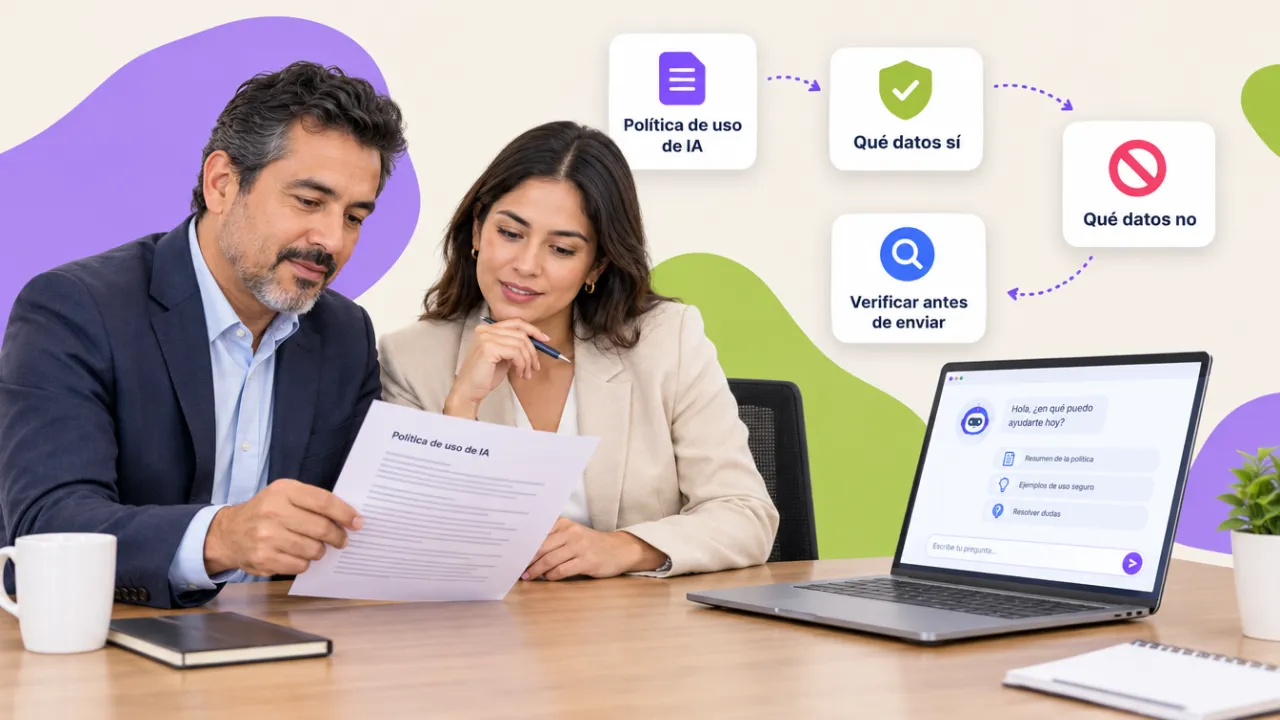
In almost every company ChatGPT or Copilot is already in use; the question is whether it is used with rules. A generative AI usage policy is not a twenty-page legal document: it is one sheet any employee understands in two minutes and that management or legal can approve in a meeting. This guide explains what it should say and ends with a template.
In this article
- What an AI usage policy is for
- The seven sections that cannot be missing
- 1. Authorized tools
- 2. Data that is never shared
- 3. Data that may be used
- 4. Mandatory verification
- 5. Transparency
- 6. Intellectual property and third-party confidentiality
- 7. Owners and review
- One-page template
- How to roll it out
- Three questions a good policy answers in seconds
- Want to bring this to your team?
What an AI usage policy is for
Three things: preventing information leaks (the most real and frequent risk), preventing something the AI made up from being sent, and protecting the company and the employee when something goes wrong. Without a policy, each person decides alone, usually with a free personal account and pasting whatever is needed. With a policy, use becomes open, consistent and auditable.
The seven sections that cannot be missing
1. Authorized tools
Which ones yes (for example, Microsoft 365 Copilot with the company account; ChatGPT on the team plan) and which ones no (free personal accounts for work matters). If the company has not decided yet, the Copilot vs ChatGPT comparison helps.
2. Data that is never shared
The concrete list: personal data of customers and employees, unpublished financial information, contracts, source code, passwords, health data, third-party information under confidentiality. If in doubt, anonymize or do not share.
3. Data that may be used
Public information, internal templates without sensitive data, your own texts to correct or summarize, aggregated or anonymized data. Saying it explicitly prevents people from abandoning the tool out of fear.
4. Mandatory verification
Everything generated is reviewed before use: figures, names, quotes, legal references and translations. AI can make things up with total confidence; responsibility for what is sent lies with the person, not the tool.
5. Transparency
When AI use is declared: in documents for customers, in reports for management, in published content. One line ("AI-assisted draft, reviewed by…") is usually enough.
6. Intellectual property and third-party confidentiality
Protected third-party texts, images or code are not entered without the right to do so, and what the AI generates is reviewed so as not to reproduce someone else's content.
7. Owners and review
Who answers questions (IT, legal, an AI owner), how incidents are reported and how often the policy is reviewed. Six months is reasonable while tools change this fast.
One-page template
| Section | Base text (adapt) |
|---|---|
| Scope | Applies to all staff using generative AI tools for work tasks. |
| Authorized tools | Copilot with the institutional account; ChatGPT team plan with data excluded from training. |
| Never share | Personal data, non-public financials, contracts, code, passwords, health data, third-party information. |
| Allowed | Public information, own texts without sensitive data, anonymized or aggregated data. |
| Verification | Every output is reviewed before use; the person is responsible for what they send. |
| Transparency | Declare use in documents for customers, management and publications. |
| Owner and review | Questions and incidents: [area]. Review every six months. |
How to roll it out
A policy nobody read does not exist. What works is presenting it in the same course where the team learns to use the tool: that way each rule connects to a practical case ("this can be pasted, this gets anonymized first") and people remember it. In the generative AI and Copilot for the office course each group leaves with its one-page policy adapted and ready to approve; for the passwords-and-leaks side, we reinforce it with the cybersecurity awareness course.
Three questions a good policy answers in seconds
An employee has a customer contract and wants AI to summarize it: the policy says the contract is on the "never share" list, so they either use the institutional tool that keeps data inside the company environment or they do not. An analyst wants to clean a spreadsheet of sales by region: aggregated data with no personal information is allowed, so they go ahead. A salesperson used AI to draft a proposal: verification is mandatory and use must be declared in documents for customers, so they check every figure and add a line. If your team cannot answer those three questions in seconds, the policy is not done yet.
Want to bring this to your team?
Each group leaves the course with its one-page AI usage policy, adapted to its tools and ready for management or legal to approve. Message us on WhatsApp, fill out the contact form or open this site's live chat: we send a proposal with three scope options and a closed price in under 24 business hours, with the DC-3 certificate and Geedle Bot included. The full program is at the generative AI and Copilot for the office course and the catalog at training courses for companies.