Meta Pixel Saltar al contenido
Logo Geedle
Toluca, State of Mexico

ISO 27001 consulting for companies in Toluca, State of Mexico

We help companies in Toluca implement an information security management system under ISO/IEC 27001:2022, with risk assessment, statement of applicability, staff awareness and internal audit.

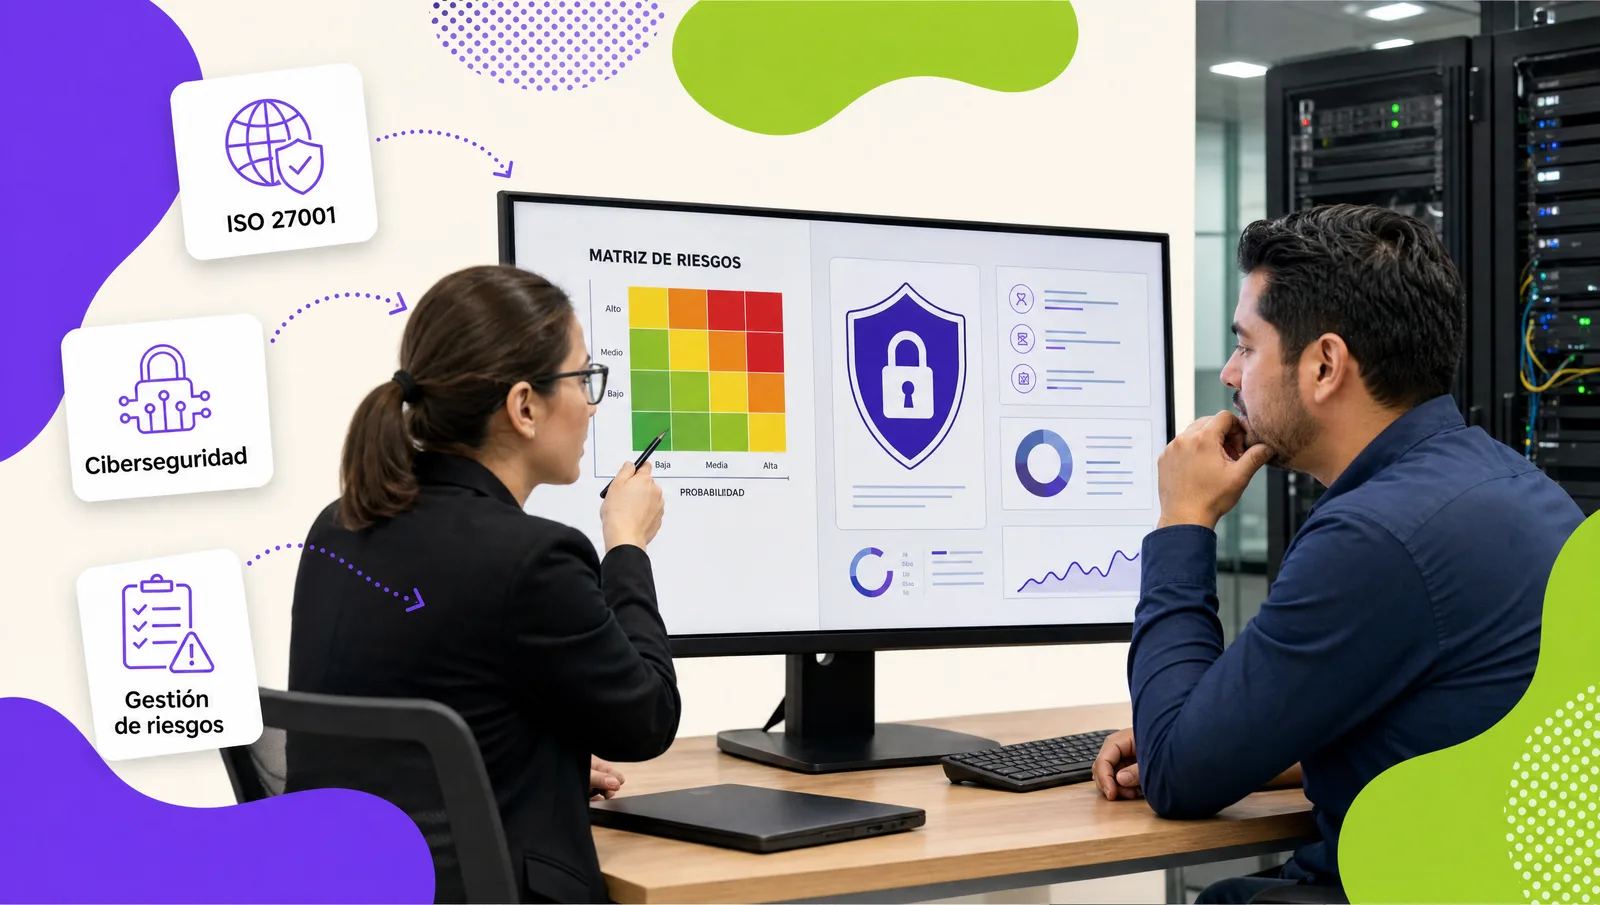
IT team and management reviewing the information security risk map in a meeting room

How do we deliver ISO 27001 consulting for organizations in Toluca?

The Toluca Valley employs thousands of people at automotive, pharmaceutical, chemical, and food plants along the Toluca-Lerma corridor, plus distribution centers, retail, and services in Metepec. Our team adapts the scope to their size and sector, works on-site when needed and online the rest of the time, and measures results from the first month.

01

Pharmaceutical, food and logistics in the Toluca-Lerma corridor

In the Toluca-Lerma corridor, pharmaceutical and food plants and distribution centers handle formulas, batch records and customer data that must be protected as carefully as the product. We implement the ISMS with a risk assessment covering plant, warehouse and office systems, and with awareness adapted to shifts and staff who share computers. We visit from Mexico City and Querétaro for workshops and the internal audit, and we review with you how the ISMS fits alongside the quality systems your customers already audit, so documentation and audits are not duplicated.

02

Coverage in Toluca and formats

We serve organizations in Toluca, Metepec, Zinacantepec, Lerma, San Mateo Atenco, and the Toluca Valley. We have a team in León and cover the Bajío from Querétaro; in the other locations we combine visits with online work. See also ISO 45001 consulting in Toluca, AI agents for business in Toluca. The full detail of the service is at iso 27001 consulting.

Why Geedle?

Six pieces of an ISMS that actually gets used

The documents you need, controls in place and people who know what to do when something fails.

Gap analysis

We compare your current situation with every requirement of the standard and prioritize what is missing by risk and effort.

Risk assessment

A clear methodology to identify assets, threats and vulnerabilities, rate the risk and decide how to treat it.

Statement of applicability

The applicable Annex A controls, the excluded ones and the justification for each, ready for the auditor.

Tailored policies

Short policies and procedures written for your real operation, not generic templates that nobody ever reads.

Measurable awareness

A cybersecurity awareness course with assessment, phishing simulations and a certificate recorded on the platform.

Internal audit

We audit the full ISMS before the certification body does and deliver findings and corrective actions.

Method

How we work in Toluca

The same stages of the method, with on-site visits when the project requires them.

  1. Gap analysis and scope

    We review processes, systems and existing documentation, and define with management which areas, sites and services the ISMS covers and what each client expects.

    Gap and scope report
  2. Risk assessment and treatment

    We inventory information assets, assess threats and vulnerabilities with each area and agree on the treatment plan with owners and dates.

    Risk matrix and treatment plan
  3. Controls, policies and SoA

    We implement the applicable Annex A controls and write short policies and the statement of applicability with the justification for each control.

    Statement of applicability
  4. Awareness and operation

    We train all staff with the cybersecurity course, put the controls into operation and generate the evidence the standard requires.

    Competence and operation records
  5. Internal audit and readiness

    We perform the internal audit, close the management review and support you during the stage 1 and stage 2 audits of the certification body.

    Internal audit report

Is your organization in Toluca ready to start?

Message us on WhatsApp, request a proposal or open the chat; we reply the same day with three scope options.

Your ISMS ready for the certification audit

Certification is granted by an accredited certification body; we get you ready to receive it with organized evidence.

  • ISMS scope approved by management
  • Current risk assessment and treatment plan
  • Statement of applicability with Annex A controls
  • Trained staff with certificates on the platform
  • Internal audit and management review closed
Information security officer reviewing the statement of applicability before the audit

Implementing with support versus doing it alone

Both routes reach the standard; the difference is time and what is left running.

With GeedleOn your own
Starting pointGap analysis against every requirementReading the standard and downloaded templates
Risk assessmentProven methodology and workshops with each areaSpreadsheets that get abandoned
Statement of applicabilityControls justified for your operationA list copied from Annex A
AwarenessCourse with assessment and certificate on the platformOne yearly talk with no records
Internal auditAuditors experienced in management systemsReview by the same team that implemented
MaintenanceReview calendar and continual improvementThe ISMS freezes after the certificate
FAQ

Frequently asked questions about iSO 27001 consulting in Toluca

Let's talk about your project in Toluca

Tell us about your case by WhatsApp, form or chat. We reply the same day, free and with no commitment.